Technology & Security
Knock delivers HIPAA-safe clinical messages inside the tools clinicians already use — iMessage and SMS — with end-to-end encryption and zero PHI ever placed in the text.
The stack
Four layers, each chosen so a secure message can travel from one clinician to another without a new app to learn.
Architecture
Watch the flow: content is encrypted on the sender's device, relayed through the Knock API, and revealed only to an authenticated recipient — the carrier only ever sees a link.
encrypt on device → ciphertext to API → link over iMessage/SMS → biometric unlock → decrypt & read
Hosting & regions
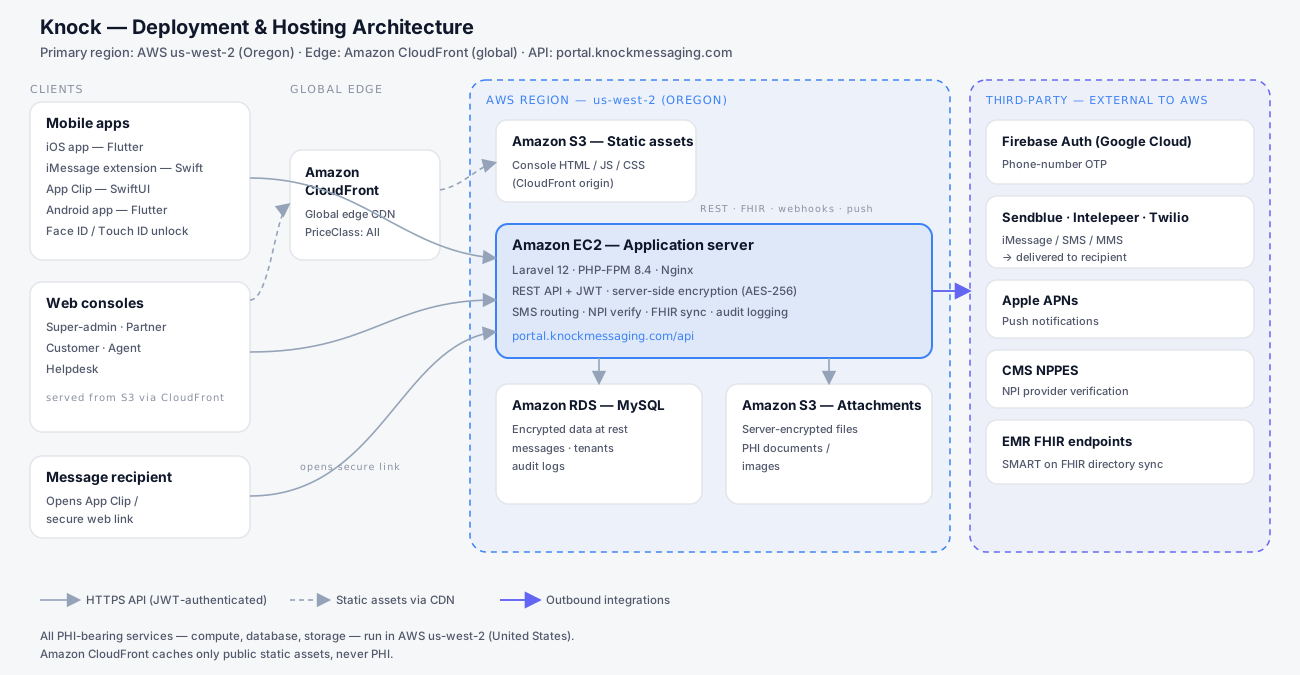
Knock is hosted on Amazon Web Services. Every service that stores or processes PHI lives in a single United States region — us-west-2 (Oregon) — with Amazon CloudFront serving only public static assets from a global edge network.
The Laravel API runs on Amazon EC2 behind Nginx.
Structured data on managed Amazon RDS (MySQL), encrypted at rest.
Amazon S3 holds server-encrypted attachments and the static console assets.
Amazon CloudFront serves the public site & web consoles worldwide — origin in us-west-2. No PHI is cached.
GitHub Actions deploys over SSH, opening the EC2 security group only for the runner's IP, then revoking it.
Called outbound from the API for auth, delivery and lookups.
Data residency. All PHI-bearing services — compute, database and storage — run in AWS us-west-2 (United States). CloudFront's global edge caches only public static assets, never protected health information.
Data model
A high-level view of the core entities and how they relate — messaging on one side, the multi-tenant SMS service on the other.
10+ tables · MySQL on AWS RDS · migrations-versioned
Encryption
Every message is end-to-end encrypted. The plaintext never touches the carrier, the SMS, or an unauthenticated screen — only a link does.
Each user gets an RSA-2048 key pair created on-device. The private key never leaves the phone; only the public key is shared with the server.
The message body is encrypted with a one-time AES-256-CBC key, which is then wrapped with the recipient's public key.
iMessage/SMS carry a secure App Clip link — never PHI. The bubble simply reads “New Message · Knock Encrypted.”
The recipient authenticates with Face ID / Touch ID; the message is decrypted on-device. Keys are shared app↔extension via a secure iOS App Group.
Safeguards
PHI & HIPAA
A plain-language summary of how Knock handles Protected Health Information and the standard practices it follows — written so you can copy it straight into a security review or vendor questionnaire.
Knock is designed to the HIPAA Security Rule. Protected Health Information (PHI) is encrypted end to end, is never placed in a text message, and is disclosed only to an authenticated, biometric-verified recipient.